Zurück   Trojaner-Board > Malware entfernen > Plagegeister aller Art und deren Bekämpfung

Plagegeister aller Art und deren Bekämpfung: Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren!

Windows 7 Wenn Du nicht sicher bist, ob Du dir Malware oder Trojaner eingefangen hast, erstelle hier ein Thema. Ein Experte wird sich mit weiteren Anweisungen melden und Dir helfen die Malware zu entfernen oder Unerwünschte Software zu deinstallieren bzw. zu löschen. Bitte schildere dein Problem so genau wie möglich. Sollte es ein Trojaner oder Viren Problem sein wird ein Experte Dir bei der Beseitigug der Infektion helfen.

Antwort
Alt 04.11.2009, 17:11   #1
Vanelein
 
Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren! - Standard

Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren!


Hallo meine Lieben,

hier meldet sich ein absoluter Computer-nicht-checker und habe folgendes Problem. Ich bekomme andauernd Virenmeldungen zu viele um jetzt jeden einzelnen zu nennen aber das größte Problme ist dieser hier

"TR/Crypt.ZPACK.Gen"

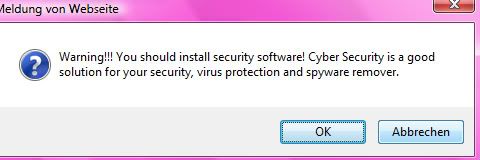
und es öffnet sich andauernd mein Internet-Explorer so das ich nur kurz in meinem Mozilla surfen kann und dann wird das immer geöffnet:


Desweiteren habe ich nur noch eingeschränkte Administrationsrechte....

So und nun hab ich alles mal abgearbeitet wies in der Anleitung stand:

Geändert von Vanelein (04.11.2009 um 17:33 Uhr)

Alt 04.11.2009, 17:15   #2
Vanelein
 
Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren! - Standard

Teil 1


So hab alles schon abgearbeitet:

PHP-Code:
Logfile of random's system information tool 1.06 (written by random/random)
Run by ***** at 2009-11-04 16:46:11
Microsoft® Windows Vista™ Home Premium  Service Pack 1
System drive C: has 69 GB (47%) free of 148 GB
Total RAM: 3066 MB (52% free)

Logfile of Trend Micro HijackThis v2.0.2
Scan saved at 16:46:53, on 04.11.2009
Platform: Windows Vista SP1 (WinNT 6.00.1905)
MSIE: Internet Explorer v8.00 (8.00.6001.18828)
Boot mode: Normal

Running processes:
C:\Windows\system32\taskeng.exe
C:\Program Files\Samsung\EBM\EasyBatteryMgr3.exe
C:\Program Files\Samsung\Samsung Magic Doctor\MagicDoctorKbdHk.exe
C:\Program Files\Samsung\Easy Display Manager\dmhkcore.exe
C:\Program Files\SAMSUNG\EasySpeedUpManager\EasySpeedUpManager.exe
C:\Windows\system32\Dwm.exe
C:\Windows\Explorer.EXE
C:\Program Files\Windows Defender\MSASCui.exe
C:\Windows\RtHDVCpl.exe
C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
C:\Program Files\CyberLink\PowerDVD\PDVDServ.exe
C:\Program Files\Windows Live\Family Safety\fsui.exe
C:\Program Files\iTunes\iTunesHelper.exe
C:\Program Files\Search Settings\SearchSettings.exe
C:\Program Files\Java\jre6\bin\jusched.exe
C:\Program Files\Avira\AntiVir Desktop\avgnt.exe
C:\Program Files\Windows Sidebar\sidebar.exe
C:\Program Files\Common Files\LightScribe\LightScribeControlPanel.exe
C:\Program Files\Electronic Arts\EADM\Core.exe
C:\Program Files\IncrediMail\Bin\IncMail.exe
C:\Program Files\Windows Media Player\wmpnscfg.exe
C:\Program Files\WIDCOMM\Bluetooth Software\BTTray.exe
C:\Program Files\IncrediMail\bin\IMApp.exe
C:\Program Files\Synaptics\SynTP\SynTPHelper.exe
C:\Windows\system32\wuauclt.exe
C:\Windows\system32\conime.exe
C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
C:\Program Files\Malwarebytes' 
Anti-Malware\mbam.exe
C
:\Program Files\Mozilla Firefox\firefox.exe
C
:\Users\Max Musterman\Desktop\RSIT.exe
C
:\Windows\system32\SearchFilterHost.exe
C
:\Program Files\trend micro\Max Musterman.exe

R1 
- HKCU\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http:\\www.samsungcomputer.com
R1 
- HKCU\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = http://mystart.incredimail.com/
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http:\\www.samsungcomputer.com
R1 
- HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,SearchAssistant = 
R0 - HKLM\Software\Microsoft\Internet Explorer\Search,CustomizeSearch = 
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = *.local
R0 
- HKCU\Software\Microsoft\Internet Explorer\Toolbar,LinksFolderName = 
R3 - URLSearchHook: (no name) -  - (no file)
R3 - URLSearchHook: SearchSettings Class - {E312764E-7706-43F1-8DAB-FCDD2B1E416D} - C:\Program Files\Search Settings\kb128\SearchSettings.dll
O1 
- Hosts: ::1 localhost
O2 
- BHO: (no name) - {03B3276E-B5E7-4535-B83A-60DABC949AD8} - C:\Windows\System32\cryptnet32.dll
O2 
- BHO: Adobe PDF Reader - {06849E9F-C8D7-4D59-B87D-784B7D6BE0B3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelper.dll
O2 
- BHO: Windows Live Family Safety Browser Helper - {4f3ed5cd-0726-42a9-87f5-d13f3d2976ac} - C:\Program Files\Windows Live\Family Safety\fssbho.dll
O2 
- BHO: Spybot-S&D IE Protection - {53707962-6F74-2D53-2644-206D7942484F} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O2 
- BHO: (no name) - {5C255C8A-E604-49b4-9D64-90988571CECB} - (no file)
O2 - BHO: Search Helper - {6EBF7485-159F-4bff-A14F-B9E3AAC4465B} - C:\Program Files\Microsoft\Search Enhancement Pack\Search Helper\SEPsearchhelperie.dll
O2 
- BHO: Windows Live Anmelde-Hilfsprogramm - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O2 
- BHO: Java(tm) Plug-In 2 SSV Helper - {DBC80044-A445-435b-BC74-9C25C1C588A9} - C:\Program Files\Java\jre6\bin\jp2ssv.dll
O2 
- BHO: Windows Live Toolbar Helper - {E15A8DC0-8516-42A1-81EA-DC94EC1ACF10} - C:\Program Files\Windows Live\Toolbar\wltcore.dll
O2 
- BHO: SearchSettings Class - {E312764E-7706-43F1-8DAB-FCDD2B1E416D} - C:\Program Files\Search Settings\kb128\SearchSettings.dll
O2 
- BHO: kikin Plugin - {E601996F-E400-41CA-804B-CD6373A7EEE2} - C:\Program Files\kikin\ie_kikin.dll
O3 
- Toolbar: &Windows Live Toolbar - {21FA44EF-376D-4D53-9B0F-8A89D3229068} - C:\Program Files\Windows Live\Toolbar\wltcore.dll
O4 
- HKLM\..\Run: [Windows Defender] %ProgramFiles%\Windows Defender\MSASCui.exe -hide
O4 
- HKLM\..\Run: [RtHDVCpl] RtHDVCpl.exe
O4 
- HKLM\..\Run: [SynTPEnh] C:\Program Files\Synaptics\SynTP\SynTPEnh.exe
O4 
- HKLM\..\Run: [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 8.0\Reader\Reader_sl.exe"
O4 - HKLM\..\Run: [RemoteControl] "C:\Program Files\CyberLink\PowerDVD\PDVDServ.exe"
O4 - HKLM\..\Run: [LanguageShortcut] "C:\Program Files\CyberLink\PowerDVD\Language\Language.exe"
O4 - HKLM\..\Run: [fssui] "C:\Program Files\Windows Live\Family Safety\fsui.exe" -autorun
O4 
- HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\QTTask.exe" -atboottime
O4 
- HKLM\..\Run: [iTunesHelper] "C:\Program Files\iTunes\iTunesHelper.exe"
O4 - HKLM\..\Run: [SearchSettings] C:\Program Files\Search Settings\SearchSettings.exe
O4 
- HKLM\..\Run: [NvCplDaemon] RUNDLL32.EXE C:\Windows\system32\NvCpl.dll,NvStartup
O4 
- HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Java\jre6\bin\jusched.exe"
O4 - HKLM\..\Run: [avgnt] "C:\Program Files\Avira\AntiVir Desktop\avgnt.exe" /min
O4 
- HKLM\..\RunOnce: [Malwarebytes' Anti-Malware] C:\Program Files\Malwarebytes' Anti-Malware\mbamgui.exe /install /silent
O4 
- HKCU\..\Run: [Sidebar] C:\Program Files\Windows Sidebar\sidebar.exe /autoRun
O4 
- HKCU\..\Run: [WindowsWelcomeCenter] rundll32.exe oobefldr.dll,ShowWelcomeCenter
O4 
- HKCU\..\Run: [LightScribe Control Panel] C:\Program Files\Common Files\LightScribe\LightScribeControlPanel.exe -hidden
O4 
- HKCU\..\Run: [EA Core] "C:\Program Files\Electronic Arts\EADM\Core.exe" -silent
O4 
- HKCU\..\Run: [IncrediMail] C:\Program Files\IncrediMail\bin\IncMail.exe /c
O4 
- HKCU\..\Run: [SpybotSD TeaTimer] C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe
O4 
- HKCU\..\Run: [WMPNSCFG] C:\Program Files\Windows Media Player\WMPNSCFG.exe
O4 
- HKUS\S-1-5-19\..\Run: [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /detectMem (User 'LOKALER DIENST')
O4 - HKUS\S-1-5-19\..\Run: [WindowsWelcomeCenter] rundll32.exe oobefldr.dll,ShowWelcomeCenter (User 'LOKALER DIENST')
O4 - HKUS\S-1-5-20\..\Run: [Sidebar] %ProgramFiles%\Windows Sidebar\Sidebar.exe /detectMem (User 'NETZWERKDIENST')
O4 - Global Startup: BTTray.lnk = ?
O8 - Extra context menu item: Nach Microsoft &Excel exportieren - res://C:\PROGRA~1\MICROS~2\OFFICE11\EXCEL.EXE/3000
O8 - Extra context menu item: Nach Microsoft E&xel exportieren - res://C:\PROGRA~1\MICROS~2\Office12\EXCEL.EXE/3000
O9 - Extra button: (no name) - {0F7195C2-6713-4d93-A1BC-DA5FA33F0A65} - C:\Program Files\kikin\ie_kikin.dll
O9 
- Extra 'Tools' menuitem: My kikin - {0F7195C2-6713-4d93-A1BC-DA5FA33F0A65} - C:\Program Files\kikin\ie_kikin.dll
O9 
- Extra button: In Blog veröffentlichen - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 
- Extra 'Tools' menuitem: In Windows Live Writer in Blog veröffentliche&n - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 
- Extra button: Recherchieren - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~1\MICROS~2\OFFICE11\REFIEBAR.DLL
O9 
- Extra button: @btrez.dll,-4015 - {CCA281CA-C863-46ef-9331-5C8D4460577F} - C:\Program Files\WIDCOMM\Bluetooth Software\btsendto_ie.htm
O9 
- Extra 'Tools' menuitem: @btrez.dll,-12650 - {CCA281CA-C863-46ef-9331-5C8D4460577F} - C:\Program Files\WIDCOMM\Bluetooth Software\btsendto_ie.htm
O9 
- Extra button: (no name) - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O9 
- Extra 'Tools' menuitem: Spybot - Search & Destroy Configuration - {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - C:\PROGRA~1\SPYBOT~1\SDHelper.dll
O9 
- Extra button: ICQ6 - {E59EB121-F339-4851-A3BA-FE49C35617C2} - C:\Program Files\ICQ6.5\ICQ.exe
O9 
- Extra 'Tools' menuitem: ICQ6 - {E59EB121-F339-4851-A3BA-FE49C35617C2} - C:\Program Files\ICQ6.5\ICQ.exe
O13 
- Gopher Prefix: 
O16 - DPF: {D0C0F75C-683A-4390-A791-1ACFD5599AB8} (Oberon Flash Game Host) - http://icq.oberon-media.com/Gameshell/GameHost/1.0/OberonGameHost.cab
O18 - Protocol: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - C:\PROGRA~1\COMMON~1\Skype\SKYPE4~1.DLL
O20 
- AppInit_DLLs: C:\Windows\System32\cryptdlg32.dll
O23 
- Service: Avira AntiVir Planer (AntiVirSchedulerService) - Avira GmbH - C:\Program Files\Avira\AntiVir Desktop\sched.exe
O23 
- Service: Avira AntiVir Guard (AntiVirService) - Avira GmbH - C:\Program Files\Avira\AntiVir Desktop\avguard.exe
O23 
- Service: Apple Mobile Device - Apple Inc. - C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
O23 
- Service: Bonjour-Dienst (Bonjour Service) - Apple Inc. - C:\Program Files\Bonjour\mDNSResponder.exe
O23 
- Service: Intel® PROSet/Wireless Event Log (EvtEng) - Intel(R) Corporation - C:\Program Files\Intel\WiFi\bin\EvtEng.exe
O23 
- Service: FLEXnet Licensing Service - Macrovision Europe Ltd. - C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe
O23 
- Service: iPod-Dienst (iPod Service) - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 
- Service: LightScribeService Direct Disc Labeling Service (LightScribeService) - Hewlett-Packard Company - C:\Program Files\Common Files\LightScribe\LSSrvc.exe
O23 
- Service: NVIDIA Display Driver Service (nvsvc) - NVIDIA Corporation - C:\Windows\system32\nvvsvc.exe
O23 
- Service: Intel® PROSet/Wireless Registry Service (RegSrvc) - Intel(R) Corporation - C:\Program Files\Common Files\Intel\WirelessCommon\RegSrvc.exe
O23 
- Service: Cyberlink RichVideo Service(CRVS) (RichVideo) - Unknown owner - C:\Program Files\CyberLink\Shared Files\RichVideo.exe
O23 
- Service: Samsung Update Plus - Unknown owner - C:\Program Files\Samsung\Samsung Update Plus\SLUBackgroundService.exe
O23 
- Service: SBSD Security Center Service (SBSDWSCService) - Safer Networking Ltd. - C:\Program Files\Spybot - Search & Destroy\SDWinSec.exe

--
End of file - 10562 bytes

======Scheduled tasks folder======

C:\Windows\tasks\User_Feed_Synchronization-{0203ACB7-A4C8-4F2B-AA3E-B1CA1108824B}.job

======Registry dump======

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{03B3276E-B5E7-4535-B83A-60DABC949AD8}]
C:\Windows\System32\cryptnet32.dll [2009-10-29 268288]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{06849E9F-C8D7-4D59-B87D-784B7D6BE0B3}]
Adobe PDF Reader - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelper.dll [2006-10-22 62080]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{4f3ed5cd-0726-42a9-87f5-d13f3d2976ac}]
Windows Live Family Safety Browser Helper Class - C:\Program Files\Windows Live\Family Safety\fssbho.dll [2009-02-06 61808]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{53707962-6F74-2D53-2644-206D7942484F}]
Spybot-S&D IE Protection - C:\PROGRA~1\SPYBOT~1\SDHelper.dll [2009-01-26 1879896]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{5C255C8A-E604-49b4-9D64-90988571CECB}]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{6EBF7485-159F-4bff-A14F-B9E3AAC4465B}]
Search Helper - C:\Program Files\Microsoft\Search Enhancement Pack\Search Helper\SEPsearchhelperie.dll [2009-05-19 137600]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{9030D464-4C02-4ABF-8ECC-5164760863C6}]
Windows Live Anmelde-Hilfsprogramm - C:\Program Files\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll [2009-01-22 408448]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{DBC80044-A445-435b-BC74-9C25C1C588A9}]
Java(tm) Plug-In 2 SSV Helper - C:\Program Files\Java\jre6\bin\jp2ssv.dll [2009-03-09 35840]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{E15A8DC0-8516-42A1-81EA-DC94EC1ACF10}]
Windows Live Toolbar Helper - C:\Program Files\Windows Live\Toolbar\wltcore.dll [2009-02-06 1068904]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{E312764E-7706-43F1-8DAB-FCDD2B1E416D}]
SearchSettings Class - C:\Program Files\Search Settings\kb128\SearchSettings.dll [2009-04-09 1091584]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{E601996F-E400-41CA-804B-CD6373A7EEE2}]
kikin Plugin - C:\Program Files\kikin\ie_kikin.dll [2009-07-14 429280]

[
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Internet Explorer\Toolbar]
{
21FA44EF-376D-4D53-9B0F-8A89D3229068} - &Windows Live Toolbar - C:\Program Files\Windows Live\Toolbar\wltcore.dll [2009-02-06 1068904]

[
HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run]
"Windows Defender"=C:\Program Files\Windows Defender\MSASCui.exe [2008-01-21 1008184]
"RtHDVCpl"=C:\Windows\RtHDVCpl.exe [2008-04-17 6111232]
"SynTPEnh"=C:\Program Files\Synaptics\SynTP\SynTPEnh.exe [2007-10-26 1029416]
"Adobe Reader Speed Launcher"=C:\Program Files\Adobe\Reader 8.0\Reader\Reader_sl.exe [2007-05-10 40048]
"RemoteControl"=C:\Program Files\CyberLink\PowerDVD\PDVDServ.exe [2007-03-14 71216]
"LanguageShortcut"=C:\Program Files\CyberLink\PowerDVD\Language\Language.exe [2007-01-08 52256]
"fssui"=C:\Program Files\Windows Live\Family Safety\fsui.exe [2009-02-06 454000]
"QuickTime Task"=C:\Program Files\QuickTime\QTTask.exe [2009-01-05 413696]
"iTunesHelper"=C:\Program Files\iTunes\iTunesHelper.exe [2009-04-02 342312]
"SearchSettings"=C:\Program Files\Search Settings\SearchSettings.exe [2009-04-09 970240]
"NvCplDaemon"=C:\Windows\system32\NvCpl.dll [2009-04-30 13781536]
"SunJavaUpdateSched"=C:\Program Files\Java\jre6\bin\jusched.exe [2009-03-09 148888]
"avgnt"=C:\Program Files\Avira\AntiVir Desktop\avgnt.exe [2009-03-02 209153]

[
HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce]
"Malwarebytes' Anti-Malware"=C:\Program Files\Malwarebytes' Anti-Malware\mbamgui.exe [2009-09-10 420176]

[HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run]
"Sidebar"=C:\Program Files\Windows Sidebar\sidebar.exe [2008-01-21 1233920]
"WindowsWelcomeCenter"=oobefldr.dll,ShowWelcomeCenter []
"LightScribe Control Panel"=C:\Program Files\Common Files\LightScribe\LightScribeControlPanel.exe [2008-03-17 2289664]
"EA Core"=C:\Program Files\Electronic Arts\EADM\Core.exe [2009-09-03 3342336]
"IncrediMail"=C:\Program Files\IncrediMail\bin\IncMail.exe [2009-07-27 271744]
"SpybotSD TeaTimer"=C:\Program Files\Spybot - Search & Destroy\TeaTimer.exe [2009-01-26 2144088]
"WMPNSCFG"=C:\Program Files\Windows Media Player\WMPNSCFG.exe [2008-01-21 202240]

C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Startup
BTTray.lnk - C:\Program Files\WIDCOMM\Bluetooth Software\BTTray.exe

[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Windows]
"AppInit_DLLS"="C:\Windows\System32\cryptdlg32.dll" 

__________________


Alt 04.11.2009, 17:16   #3
Vanelein
 
Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren! - Standard

Teil 2


PHP-Code:
[HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Policies\System]
"dontdisplaylastusername"=0
"legalnoticecaption"=
"legalnoticetext"=
"shutdownwithoutlogon"=1
"undockwithoutlogon"=1
"EnableUIADesktopToggle"=0

[HKEY_LOCAL_MACHINE\system\currentcontrolset\services\sharedaccess\parameters\firewallpolicy\standardprofile\authorizedapplications\list]

[
HKEY_LOCAL_MACHINE\system\currentcontrolset\services\sharedaccess\parameters\firewallpolicy\domainprofile\authorizedapplications\list]

[
HKEY_CURRENT_USER\software\microsoft\windows\currentversion\explorer\mountpoints2\{0099659d-72e4-11de-b189-001377ab9ae5}]
shell\1\command - G:\escro.exe
shell
\AutoRun\command - C:\Windows\system32\RunDLL32.EXE Shell32.DLL,ShellExec_RunDLL G:\escro.exe


======File associations======

.
js - edit - C:\Windows\System32\Notepad.exe %1
.js - open - C:\Windows\System32\WScript.exe "%1" %*

======List 
of files/folders created in the last 1 months======

2009-11-04 16:46:13 ----D---- C:\Program Files\trend micro
2009
-11-04 16:46:11 ----D---- C:\rsit
2009
-11-04 16:13:02 ----D---- C:\Users\Vane\AppData\Roaming\Malwarebytes
2009
-11-04 16:12:01 ----D---- C:\ProgramData\Malwarebytes
2009
-11-04 16:11:54 ----D---- C:\Program Files\Malwarebytes' Anti-Malware
2009-11-04 16:06:55 ----D---- C:\Program Files\CCleaner
2009-11-03 13:42:49 ----A---- C:\Windows\system32\occache.dll
2009-11-03 13:42:49 ----A---- C:\Windows\system32\jsproxy.dll
2009-11-03 13:42:48 ----A---- C:\Windows\system32\msfeedsbs.dll
2009-11-03 13:42:48 ----A---- C:\Windows\system32\msfeeds.dll
2009-11-03 13:42:48 ----A---- C:\Windows\system32\iepeers.dll
2009-11-03 13:42:47 ----A---- C:\Windows\system32\ieui.dll
2009-11-03 13:42:47 ----A---- C:\Windows\system32\iesetup.dll
2009-11-03 13:42:40 ----A---- C:\Windows\system32\wininet.dll
2009-11-03 13:42:40 ----A---- C:\Windows\system32\msfeedssync.exe
2009-11-03 13:42:40 ----A---- C:\Windows\system32\iernonce.dll
2009-11-03 13:42:40 ----A---- C:\Windows\system32\ie4uinit.exe
2009-11-03 13:42:39 ----A---- C:\Windows\system32\ieUnatt.exe
2009-11-03 13:42:39 ----A---- C:\Windows\system32\iesysprep.dll
2009-11-03 13:42:39 ----A---- C:\Windows\system32\iertutil.dll
2009-11-03 13:42:39 ----A---- C:\Windows\system32\iedkcs32.dll
2009-11-03 13:42:38 ----A---- C:\Windows\system32\urlmon.dll
2009-11-03 13:42:37 ----A---- C:\Windows\system32\ieframe.dll
2009-11-03 13:42:34 ----A---- C:\Windows\system32\mshtml.dll
2009-11-03 13:38:58 ----A---- C:\Windows\system32\mshtmled.dll
2009-11-03 13:38:58 ----A---- C:\Windows\system32\icardie.dll
2009-11-03 13:38:57 ----A---- C:\Windows\system32\msls31.dll
2009-11-03 13:38:57 ----A---- C:\Windows\system32\mshtmler.dll
2009-11-03 13:38:57 ----A---- C:\Windows\system32\admparse.dll
2009-11-03 13:38:56 ----A---- C:\Windows\system32\imgutil.dll
2009-11-03 13:38:56 ----A---- C:\Windows\system32\ieakeng.dll
2009-11-03 13:38:56 ----A---- C:\Windows\system32\dxtmsft.dll
2009-11-03 13:38:56 ----A---- C:\Windows\system32\corpol.dll
2009-11-03 13:38:55 ----A---- C:\Windows\system32\dxtrans.dll
2009-11-03 13:38:54 ----A---- C:\Windows\system32\msrating.dll
2009-11-03 13:38:54 ----A---- C:\Windows\system32\licmgr10.dll
2009-11-03 13:38:54 ----A---- C:\Windows\system32\inseng.dll
2009-11-03 13:38:54 ----A---- C:\Windows\system32\ieaksie.dll
2009-11-03 13:38:53 ----A---- C:\Windows\system32\webcheck.dll
2009-11-03 13:38:52 ----A---- C:\Windows\system32\WinFXDocObj.exe
2009-11-03 13:38:52 ----A---- C:\Windows\system32\wextract.exe
2009-11-03 13:38:52 ----A---- C:\Windows\system32\mstime.dll
2009-11-03 13:38:52 ----A---- C:\Windows\system32\ieakui.dll
2009-11-03 13:38:51 ----A---- C:\Windows\system32\pngfilt.dll
2009-11-03 13:38:51 ----A---- C:\Windows\system32\ieapfltr.dll
2009-11-03 13:38:51 ----A---- C:\Windows\system32\advpack.dll
2009-11-03 13:38:50 ----A---- C:\Windows\system32\vbscript.dll
2009-11-03 13:38:50 ----A---- C:\Windows\system32\jscript.dll
2009-11-03 13:38:49 ----A---- C:\Windows\system32\url.dll
2009-11-03 13:38:47 ----A---- C:\Windows\system32\SetIEInstalledDate.exe
2009-11-03 13:38:47 ----A---- C:\Windows\system32\SetDepNx.exe
2009-11-03 13:38:47 ----A---- C:\Windows\system32\RegisterIEPKEYs.exe
2009-11-03 13:38:47 ----A---- C:\Windows\system32\PDMSetup.exe
2009-11-03 13:38:47 ----A---- C:\Windows\system32\mshta.exe
2009-11-03 13:38:47 ----A---- C:\Windows\system32\iexpress.exe
2009-11-03 12:09:06 ----D---- C:\ProgramData\Spybot - Search & Destroy
2009-11-03 12:09:06 ----D---- C:\Program Files\Spybot - Search & Destroy
2009-11-03 12:08:15 ----D---- C:\ProgramData\Avira
2009-10-30 13:31:17 ----A---- C:\Windows\system32\wups2.dll
2009-10-30 13:31:17 ----A---- C:\Windows\system32\wuauclt.exe
2009-10-30 13:31:16 ----A---- C:\Windows\system32\wucltux.dll
2009-10-30 13:31:16 ----A---- C:\Windows\system32\wuaueng.dll
2009-10-30 13:30:47 ----A---- C:\Windows\system32\wups.dll
2009-10-30 13:30:47 ----A---- C:\Windows\system32\wudriver.dll
2009-10-30 13:30:47 ----A---- C:\Windows\system32\wuapi.dll
2009-10-30 13:30:41 ----A---- C:\Windows\system32\wuwebv.dll
2009-10-30 13:30:41 ----A---- C:\Windows\system32\wuapp.exe
2009-10-29 18:16:39 ----A---- C:\Windows\system32\cryptnet32.dll
2009-10-29 18:16:38 ----A---- C:\Windows\system32\mjHtwK2wfR7I6.vbs
2009-10-29 18:16:38 ----A---- C:\Windows\system32\cryptdlg32.dll
2009-10-28 20:46:41 ----D---- C:\Users\Vane\AppData\Roaming\kikin
2009-10-28 20:46:39 ----D---- C:\Program Files\kikin
2009-10-28 20:46:38 ----D---- C:\Program Files\Foto-Mosaik-Edda
2009-10-28 11:28:18 ----A---- C:\Windows\system32\wmp.dll
2009-10-28 11:28:15 ----A---- C:\Windows\system32\unregmp2.exe
2009-10-28 11:28:11 ----A---- C:\Windows\system32\wmploc.DLL
2009-10-26 22:16:19 ----D---- C:\Program Files\DVDVideoSoft
2009-10-26 22:16:19 ----D---- C:\Program Files\Common Files\DVDVideoSoft
2009-10-18 02:05:12 ----D---- C:\Windows\SQL9_KB970892_ENU
2009-10-16 07:48:08 ----A---- C:\Windows\system32\msv1_0.dll
2009-10-16 07:47:30 ----A---- C:\Windows\system32\ntkrnlpa.exe
2009-10-16 07:47:29 ----A---- C:\Windows\system32\ntoskrnl.exe
2009-10-16 07:47:07 ----A---- C:\Windows\system32\EncDec.dll
2009-10-16 07:47:05 ----A---- C:\Windows\system32\psisdecd.dll
2009-10-16 07:46:46 ----A---- C:\Windows\system32\msasn1.dll
2009-10-16 07:46:43 ----A---- C:\Windows\system32\WMSPDMOD.DLL
2009-10-12 20:20:14 ----D---- C:\ProgramData\HotbarSA
2009-10-12 20:16:38 ----D---- C:\Program Files\ShoppingReport

======List of files/folders modified in the last 1 months======

2009-11-04 16:46:27 ----D---- C:\Windows\Temp
2009-11-04 16:46:13 ----RD---- C:\Program Files
2009-11-04 16:38:16 ----D---- C:\Windows\Debug
2009-11-04 16:38:16 ----D---- C:\Windows
2009-11-04 16:28:51 ----D---- C:\Windows\system32\catroot
2009-11-04 16:28:43 ----D---- C:\Windows\winsxs
2009-11-04 16:15:43 ----SHD---- C:\System Volume Information
2009-11-04 16:12:28 ----D---- C:\Windows\system32\drivers
2009-11-04 16:12:01 ----HD---- C:\ProgramData
2009-11-04 11:11:57 ----D---- C:\Windows\System32
2009-11-04 11:11:57 ----D---- C:\Windows\inf
2009-11-04 11:11:57 ----A---- C:\Windows\system32\PerfStringBackup.INI
2009-11-03 22:48:48 ----D---- C:\Users\Vane\AppData\Roaming\Adobe
2009-11-03 17:16:09 ----D---- C:\ProgramData\Google
2009-11-03 17:16:09 ----D---- C:\Program Files\Google
2009-11-03 17:16:08 ----SHD---- C:\Windows\Installer
2009-11-03 17:16:08 ----D---- C:\Windows\Tasks
2009-11-03 15:27:14 ----D---- C:\Windows\rescache
2009-11-03 15:15:54 ----D---- C:\Windows\system32\Tasks
2009-11-03 15:08:47 ----D---- C:\Users\Vane\AppData\Roaming\LimeWire
2009-11-03 15:00:54 ----D---- C:\Program Files\Avira
2009-11-03 14:58:40 ----D---- C:\Windows\system32\migration
2009-11-03 14:58:39 ----D---- C:\Program Files\Internet Explorer
2009-11-03 14:58:38 ----D---- C:\Windows\system32\de-DE
2009-11-03 14:58:36 ----D---- C:\Windows\system32\en-US
2009-11-03 14:58:36 ----D---- C:\Windows\PolicyDefinitions
2009-11-03 13:44:17 ----D---- C:\Windows\system32\catroot2
2009-11-02 20:20:17 ----D---- C:\Windows\Prefetch
2009-11-02 19:05:24 ----D---- C:\Users\Vane\AppData\Roaming\Skype
2009-11-02 17:13:09 ----D---- C:\Users\Vane\AppData\Roaming\skypePM
2009-10-29 03:07:43 ----D---- C:\Program Files\Windows Media Player
2009-10-28 19:48:11 ----RSD---- C:\Windows\Fonts
2009-10-26 22:16:19 ----D---- C:\Program Files\Common Files
2009-10-18 02:36:26 ----D---- C:\Windows\Microsoft.NET
2009-10-18 02:35:59 ----RSD---- C:\Windows\assembly
2009-10-18 02:18:36 ----D---- C:\Windows\ehome
2009-10-18 02:18:36 ----D---- C:\Program Files\Windows Mail
2009-10-18 02:08:49 ----D---- C:\ProgramData\Microsoft Help
2009-10-18 02:05:35 ----D---- C:\Program Files\Microsoft SQL Server

======List of drivers (R=Running, S=Stopped, 0=Boot, 1=System, 2=Auto, 3=Demand, 4=Disabled)======

R1 avgio;avgio; \??\C:\Program Files\Avira\AntiVir Desktop\avgio.sys [2009-02-13 11608]
R1 avipbb;avipbb; C:\Windows\system32\DRIVERS\avipbb.sys [2009-03-30 96104]
R1 ssmdrv;ssmdrv; C:\Windows\system32\DRIVERS\ssmdrv.sys [2009-05-11 28520]
R1 StarOpen;StarOpen; C:\Windows\system32\drivers\StarOpen.sys [2009-09-14 5632]
R2 avgntflt;avgntflt; C:\Windows\system32\DRIVERS\avgntflt.sys [2009-07-28 55656]
R2 fssfltr;FssFltr; C:\Windows\system32\DRIVERS\fssfltr.sys [2009-02-06 55280]
R2 KMDFMEMIO;SAMSUNG Kernel Driver; C:\Windows\system32\DRIVERS\kmdfmemio.sys [2007-05-23 13312]
R3 athr;Atheros Extensible Wireless LAN device driver; C:\Windows\system32\DRIVERS\athr.sys [2007-09-13 755712]
R3 CmBatt;Treiber für Microsoft-ACPI-Kontrollmethodenkompatible Batterie; C:\Windows\system32\DRIVERS\CmBatt.sys [2008-01-21 14208]
R3 GEARAspiWDM;GEAR ASPI Filter Driver; C:\Windows\system32\DRIVERS\GEARAspiWDM.sys [2009-03-19 23400]
R3 IntcAzAudAddService;Service for Realtek HD Audio (WDM); C:\Windows\system32\drivers\RTKVHDA.sys [2008-04-17 2098904]
R3 MBAMSwissArmy;MBAMSwissArmy; \??\C:\Windows\system32\drivers\mbamswissarmy.sys [2009-09-10 38224]
R3 NVHDA;Service for NVIDIA High Definition Audio Driver; C:\Windows\system32\drivers\nvhda32v.sys [2009-01-22 52768]
R3 nvlddmkm;nvlddmkm; C:\Windows\system32\DRIVERS\nvlddmkm.sys [2009-04-30 9850016]
R3 SynTP;Synaptics TouchPad Driver; C:\Windows\system32\DRIVERS\SynTP.sys [2007-10-26 193456]
R3 VMC302;Vimicro Camera Service VMC302; C:\Windows\System32\Drivers\VMC302.sys [2008-04-05 242560]
R3 yukonwlh;NDIS6.0 Miniport Driver for Marvell Yukon Ethernet Controller; C:\Windows\system32\DRIVERS\yk60x86.sys [2007-12-28 298496]
S3 ab1f93ks;ab1f93ks; C:\Windows\system32\drivers\ab1f93ks.sys []
S3 AgereSoftModem;Agere Systems Soft Modem; C:\Windows\system32\DRIVERS\AGRSM.sys [2006-11-28 1161888]
S3 bcm4sbxp;Broadcom 440x 10/100 Integrated Controller XP Driver; C:\Windows\system32\DRIVERS\bcm4sbxp.sys [2006-11-02 45056]
S3 BthEnum;Bluetooth-Anforderungsblocktreiber; C:\Windows\system32\DRIVERS\BthEnum.sys [2008-01-21 19456]
S3 BthPan;Bluetooth-Gerät (PAN); C:\Windows\system32\DRIVERS\bthpan.sys [2008-01-21 92160]
S3 BTHPORT;Bluetooth-Porttreiber; C:\Windows\System32\Drivers\BTHport.sys [2008-01-21 219648]
S3 BTHUSB;USB-Treiber für Bluetooth-Funkgerät; C:\Windows\System32\Drivers\BTHUSB.sys [2008-01-21 29184]
S3 btwaudio;Bluetooth-Audiogerät; C:\Windows\system32\drivers\btwaudio.sys [2008-02-14 80424]
S3 btwavdt;Bluetooth AVDT; C:\Windows\system32\drivers\btwavdt.sys [2007-07-15 80936]
S3 btwrchid;btwrchid; C:\Windows\system32\DRIVERS\btwrchid.sys [2007-07-15 16168]
S3 drmkaud;Microsoft Kernel-DRM-Audioentschlüsselung; C:\Windows\system32\drivers\drmkaud.sys [2008-01-21 5632]
S3 HdAudAddService;Microsoft 1.1 UAA-Funktionstreiber für High Definition Audio-Dienst; C:\Windows\system32\drivers\HdAudio.sys [2006-11-02 235520]
S3 ialm;ialm; C:\Windows\system32\DRIVERS\igdkmd32.sys [2006-10-19 1380864]
S3 MSKSSRV;Microsoft Streaming Service Proxy; C:\Windows\system32\drivers\MSKSSRV.sys [2008-01-21 8192]
S3 MSPCLOCK;Microsoft Proxy für Streaming Clock; C:\Windows\system32\drivers\MSPCLOCK.sys [2008-01-21 5888]
S3 MSPQM;Microsoft Proxy für Streaming Quality Manager; C:\Windows\system32\drivers\MSPQM.sys [2008-01-21 5504]
S3 MSTEE;Microsoft Streaming Tee/Sink-to-Sink-Konvertierung; C:\Windows\system32\drivers\MSTEE.sys [2008-01-21 6016]
S3 NETw3v32;Intel(R) PRO/Wireless 3945ABG Adapter Driver for Windows Vista 32 Bit; C:\Windows\system32\DRIVERS\NETw3v32.sys [2008-01-21 2225664]
S3 NETw5v32;Intel(R) Wireless WiFi Link Adaptertreiber für Windows Vista 32-Bit; C:\Windows\system32\DRIVERS\NETw5v32.sys [2008-05-20 3663360]
S3 RFCOMM;Bluetooth-Gerät (RFCOMM-Protokoll-TDI); C:\Windows\system32\DRIVERS\rfcomm.sys [2008-02-21 50688]
S3 sscdbus;SAMSUNG USB Composite Device driver (WDM); C:\Windows\system32\DRIVERS\sscdbus.sys [2008-02-22 87936]
S3 sscdmdfl;SAMSUNG Mobile Modem Filter; C:\Windows\system32\DRIVERS\sscdmdfl.sys [2008-02-22 14976]
S3 sscdmdm;SAMSUNG Mobile Modem Drivers; C:\Windows\system32\DRIVERS\sscdmdm.sys [2008-02-22 114304]
S3 USBAAPL;Apple Mobile USB Driver; C:\Windows\System32\Drivers\usbaapl.sys [2009-03-26 36864]
S3 usbvideo;USB-Videogerät (WDM); C:\Windows\System32\Drivers\usbvideo.sys [2008-01-21 134016]
S3 WpdUsb;WpdUsb; C:\Windows\system32\DRIVERS\wpdusb.sys [2008-01-21 39936]
S3 WUDFRd;WUDFRd; C:\Windows\system32\DRIVERS\WUDFRd.sys [2008-01-21 83328]
S4 ErrDev;Microsoft Hardware Error Device Driver; C:\Windows\system32\drivers\errdev.sys [2008-01-21 6656]
S4 MegaSR;MegaSR; C:\Windows\system32\drivers\megasr.sys [2008-01-21 386616]
S4 sdbus;sdbus; C:\Windows\system32\DRIVERS\sdbus.sys [2008-01-21 88576]
S4 WmiAcpi;Microsoft Windows Management Interface for ACPI; C:\Windows\system32\drivers\wmiacpi.sys [2008-01-21 11264]

======List of services (R=Running, S=Stopped, 0=Boot, 1=System, 2=Auto, 3=Demand, 4=Disabled)======

R2 AntiVirSchedulerService;Avira AntiVir Planer; C:\Program Files\Avira\AntiVir Desktop\sched.exe [2009-05-13 108289]
R2 AntiVirService;Avira AntiVir Guard; C:\Program Files\Avira\AntiVir Desktop\avguard.exe [2009-07-21 185089]
R2 Apple Mobile Device;Apple Mobile Device; C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe [2009-03-26 132424]
R2 BcmSqlStartupSvc;SQL Server-Startdienst für Business Contact Manager; C:\Program Files\Microsoft Small Business\Business Contact Manager\BcmSqlStartupSvc.exe [2008-01-16 30312]
R2 Bonjour Service;Bonjour-Dienst; C:\Program Files\Bonjour\mDNSResponder.exe [2008-12-12 238888]
R2 BthServ;@%SystemRoot%\System32\bthserv.dll,-101; C:\Windows\system32\svchost.exe [2008-01-21 21504]
R2 EvtEng;Intel® PROSet/Wireless Event Log; C:\Program Files\Intel\WiFi\bin\EvtEng.exe [2008-05-23 819200]
R2 fsssvc;Windows Live Family Safety; C:\Program Files\Windows Live\Family Safety\fsssvc.exe [2009-02-06 533360]
R2 LightScribeService;LightScribeService Direct Disc Labeling Service; C:\Program Files\Common Files\LightScribe\LSSrvc.exe [2008-03-17 73728]
R2 nvsvc;NVIDIA Display Driver Service; C:\Windows\system32\nvvsvc.exe [2009-04-30 211488]
R2 RegSrvc;Intel® PROSet/Wireless Registry Service; C:\Program Files\Common Files\Intel\WirelessCommon\RegSrvc.exe [2008-05-23 466944]
R2 RichVideo;Cyberlink RichVideo Service(CRVS); C:\Program Files\CyberLink\Shared Files\RichVideo.exe [2006-12-19 272024]
R2 SBSDWSCService;SBSD Security Center Service; C:\Program Files\Spybot - Search & Destroy\SDWinSec.exe [2009-01-26 1153368]
R2 SeaPort;SeaPort; C:\Program Files\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe [2009-05-19 240512]
R2 SQLBrowser;SQL Server-Browser; C:\Program Files\Microsoft SQL Server\90\Shared\sqlbrowser.exe [2008-11-24 239968]
R2 SQLWriter;SQL Server VSS Writer; C:\Program Files\Microsoft SQL Server\90\Shared\sqlwriter.exe [2008-11-24 87904]
R3 iPod Service;iPod-Dienst; C:\Program Files\iPod\bin\iPodService.exe [2009-04-02 656168]
S2 Samsung Update Plus;Samsung Update Plus; C:\Program Files\Samsung\Samsung Update Plus\SLUBackgroundService.exe [2008-05-13 77480]
S3 FLEXnet Licensing Service;FLEXnet Licensing Service; C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe [2009-01-09 654848]
S3 MSSQL$MSSMLBIZ;SQL Server (MSSMLBIZ); C:\Program Files\Microsoft SQL Server\MSSQL.1\MSSQL\Binn\sqlservr.exe [2009-05-27 29262680]
S3 odserv;Microsoft Office Diagnostics Service; C:\Program Files\Common Files\Microsoft Shared\OFFICE12\ODSERV.EXE [2007-08-24 443776]
S3 ose;Office Source Engine; C:\Program Files\Common Files\Microsoft Shared\Source Engine\OSE.EXE [2006-10-26 145184]
S4 MSSQLServerADHelper;Hilfsdienst von SQL Server für Active Directory; C:\Program Files\Microsoft SQL Server\90\Shared\sqladhlp90.exe [2008-11-24 45408]

-----------------EOF----------------- 
__________________

Alt 04.11.2009, 17:19   #4
Vanelein
 
Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren! - Standard

Teil 3


info-editor:

PHP-Code:
info.txt logfile of random's system information tool 1.06 2009-11-04 16:47:01

======Uninstall list======

-->MsiExec /X{DD1865F0-AD73-40FB-B23E-1822E02396FF}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-0015-0407-0000-0000000FF1CE} /uninstall {DCBECE36-8F23-4B33-925E-A1C6183C0DBD}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-0016-0407-0000-0000000FF1CE} /uninstall {DCBECE36-8F23-4B33-925E-A1C6183C0DBD}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-0018-0407-0000-0000000FF1CE} /uninstall {DCBECE36-8F23-4B33-925E-A1C6183C0DBD}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-0019-0407-0000-0000000FF1CE} /uninstall {DCBECE36-8F23-4B33-925E-A1C6183C0DBD}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-001A-0407-0000-0000000FF1CE} /uninstall {DCBECE36-8F23-4B33-925E-A1C6183C0DBD}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-001B-0407-0000-0000000FF1CE} /uninstall {DCBECE36-8F23-4B33-925E-A1C6183C0DBD}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-001F-0407-0000-0000000FF1CE} /uninstall {2AB528A5-BB1B-4EBE-8E51-AD0C4CD33CA9}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-001F-0409-0000-0000000FF1CE} /uninstall {3EC77D26-799B-4CD8-914F-C1565E796173}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-001F-040C-0000-0000000FF1CE} /uninstall {430971B1-C31E-45DA-81E0-72C095BAB72C}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-001F-0410-0000-0000000FF1CE} /uninstall {58FC5E37-DD28-4D4A-A549-125744C6763C}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {90120000-006E-0407-0000-0000000FF1CE} /uninstall {888B9AC7-8F5C-456B-A27A-157A6C310E52}
2007 Microsoft Office Suite Service Pack 1 (SP1)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {BEE75E01-DD3F-4D5F-B96C-609E6538D419}
2007 Microsoft Office system-->"C:\Program Files\Common Files\Microsoft Shared\OFFICE12\Office Setup Controller\setup.exe" /uninstall PROHYBRIDR /dll OSETUP.DLL
Activation Assistant for the 2007 Microsoft Office suites-->"C:\ProgramData\{623D32E9-0C62-4453-AD44-98B31F52A5E1}\Microsoft Office Activation Assistant.exe" REMOVE=TRUE MODIFY=FALSE
Adobe Anchor Service CS3-->MsiExec.exe /I{90176341-0A8B-4CCC-A78D-F862228A6B95}
Adobe Asset Services CS3-->MsiExec.exe /I{6FF5DD7A-FE28-4439-B8CF-1E9AF4EA0A61}
Adobe Bridge CS3-->MsiExec.exe /I{9C9824D9-9000-4373-A6A5-D0E5D4831394}
Adobe Bridge Start Meeting-->MsiExec.exe /I{08B32819-6EEF-4057-AEDA-5AB681A36A23}
Adobe Camera Raw 4.0-->MsiExec.exe /I{B3BF6689-A81D-40D8-9A86-4AC4ACD9FC1C}
Adobe CMaps-->MsiExec.exe /I{A2B242BD-FF8D-4840-9DAA-9170EABEC59C}
Adobe Color - Photoshop Specific-->MsiExec.exe /I{A2D81E70-2A98-4A08-A628-94388B063C5E}
Adobe Color Common Settings-->MsiExec.exe /I{DADD7B8A-BCB0-44F5-967A-ECB6B4F2ECD9}
Adobe Color EU Recommended Settings-->MsiExec.exe /I{73B5D990-04EA-4751-B10F-5534770B91F2}
Adobe Color JA Extra Settings-->MsiExec.exe /I{DD7DB3C5-6FA3-4FA3-8A71-C2F2940EB029}
Adobe Color NA Extra Settings-->MsiExec.exe /I{FF29A7E2-FF40-4D07-B7E4-2093DE59E10A}
Adobe Default Language CS3-->MsiExec.exe /I{B9B35331-B7E4-4E5C-BF4C-7BC87856124D}
Adobe Device Central CS3-->MsiExec.exe /I{8D2BA474-F406-4710-9AE4-D4F22D21F0DD}
Adobe ExtendScript Toolkit 2-->MsiExec.exe /I{C2D69781-F392-4118-A5A7-C7E9C38DBFC2}
Adobe Flash Player 10 ActiveX-->C:\Windows\system32\Macromed\Flash\uninstall_activeX.exe
Adobe Flash Player 10 Plugin-->C:\Windows\system32\Macromed\Flash\uninstall_plugin.exe
Adobe Fonts All-->MsiExec.exe /I{6ABE0BEE-D572-4FE8-B434-9E72A289431B}
Adobe Help Viewer CS3-->MsiExec.exe /I{04AF207D-9A77-465A-8B76-991F6AB66245}
Adobe Linguistics CS3-->MsiExec.exe /I{54793AA1-5001-42F4-ABB6-C364617C6078}
Adobe PDF Library Files-->MsiExec.exe /I{D2559B88-CC9D-4B48-81BB-F492BAA9C48C}
Adobe Photoshop CS3-->C:\Program Files\Common Files\Adobe\Installers\5f143314a5d434c8511097393d17397\Setup.exe
Adobe Photoshop CS3-->MsiExec.exe /I{D3C605D8-3A5E-4BAD-965D-2C61441BF2AC}
Adobe Reader 8.1.0 - Deutsch-->MsiExec.exe /I{AC76BA86-7AD7-1031-7B44-A81000000003}
Adobe Setup-->MsiExec.exe /I{B582947F-F34D-4081-A5B9-24CBF09F8C15}
Adobe Shockwave Player-->C:\Windows\System32\Adobe\SHOCKW~1\UNWISE.EXE C:\Windows\System32\Adobe\SHOCKW~1\Install.log
Adobe Stock Photos CS3-->MsiExec.exe /I{29E5EA97-5F74-4A57-B8B2-D4F169117183}
Adobe Type Support-->MsiExec.exe /I{8E6808E2-613D-4FCD-81A2-6C8FA8E03312}
Adobe Update Manager CS3-->MsiExec.exe /I{E69AE897-9E0B-485C-8552-7841F48D42D8}
Adobe Version Cue CS3 Client-->MsiExec.exe /I{D0DFF92A-492E-4C40-B862-A74A173C25C5}
Adobe WinSoft Linguistics Plugin-->MsiExec.exe /I{184CE391-7E0E-4C63-9935-D7A10EDFD3C6}
Adobe XMP Panels CS3-->MsiExec.exe /I{802771A9-A856-4A41-ACF7-1450E523C923}
Agere Systems HDA Modem-->agrsmdel
Apple Mobile Device Support-->MsiExec.exe /I{AFA20D47-69C3-4030-8DF8-D37466E70F13}
Apple Software Update-->MsiExec.exe /I{6956856F-B6B3-4BE0-BA0B-8F495BE32033}
Atheros WLAN Client-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\PROFES~1\RunTime\0701\Intel32\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{04983D37-2202-4295-94A2-8B547C66133F}\setup.exe" -l0x9 
Avira AntiVir Personal - Free Antivirus-->C:\Program Files\Avira\AntiVir Desktop\setup.exe /REMOVE
Bonjour-->MsiExec.exe /I{07287123-B8AC-41CE-8346-3D777245C35B}
Business Contact Manager für Outlook 2007 SP1-->"C:\Program Files\Microsoft Small Business\Business Contact Manager\SetupBootstrap\Setup.exe" /remove {4cb9f93c-9edc-4be9-ae61-af128ddbecfa}
Business Contact Manager für Outlook 2007 SP1-->MsiExec.exe /X{4CB9F93C-9EDC-4BE9-AE61-AF128DDBECFA}
CCleaner-->"C:\Program Files\CCleaner\uninst.exe"
Choice Guard-->MsiExec.exe /I{8FFC5648-FAF8-43A3-BC8F-42BA1E275C4E}
CyberLink DVD Suite-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\engine\6\INTEL3~1\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{1FBF6C24-C1FD-4101-A42B-0C564F9E8E79}\setup.exe"  -uninstall
CyberLink Power2Go-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\engine\6\INTEL3~1\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{40BF1E83-20EB-11D8-97C5-0009C5020658}\setup.exe"  -uninstall
Die Sims™ 3-->"C:\Program Files\InstallShield Installation Information\{C05D8CDB-417D-4335-A38C-A0659EDFD6B8}\setup.exe" -runfromtemp -l0x0007 -removeonly
DivX Codec-->C:\Program Files\DivX\DivXCodecUninstall.exe /CODEC
DivX Player-->C:\Program Files\DivX\DivXPlayerUninstall.exe /PLAYER
DivX Web Player-->C:\Program Files\DivX\DivXWebPlayerUninstall.exe /PLUGIN
EA Download Manager-->C:\Program Files\Electronic Arts\EADM\Uninstall.exe
Easy Battery Manager-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\PROFES~1\RunTime\0701\Intel32\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{6F730513-8688-4C3C-90A3-6B9792CE2EF3}\setup.exe" -l0x9 Remove
Easy Display Manager-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\PROFES~1\RunTime\10\00\Intel32\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{17283B95-21A8-4996-97DA-547A48DB266F}\setup.exe" -l0x9  -removeonly
Easy Network Manager 3.0-->C:\Program Files\InstallShield Installation Information\{4EA8EA5D-8E46-4698-9BF7-2F2AD8E1C185}\setup.exe -runfromtemp -l0x0407
Easy SpeedUp Manager-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\PROFES~1\RunTime\0701\Intel32\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{EF367AA4-070B-493C-9575-85BE59D789C9}\setup.exe" -l0x9 Remove
ElsterFormular 2008/2009-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\PROFES~1\RunTime\11\50\Intel32\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{04830D0F-F980-4EC0-89F1-594F2FD2A1B5}\setup.exe" -l0x7  -removeonly
Foto-Mosaik-Edda 5.5.0-->"C:\Program Files\Foto-Mosaik-Edda\unins000.exe"
Free Audio CD Burner version 1.2-->"C:\Program Files\DVDVideoSoft\Free Audio CD Burner\unins000.exe"
Free YouTube to MP3 Converter version 3.2-->"C:\Program Files\DVDVideoSoft\Free YouTube to MP3 Converter\unins000.exe"
GDR 4053 for SQL Server Database Services 2005 ENU (KB970892)-->C:\Windows\SQL9_KB970892_ENU\Hotfix.exe /Uninstall
HijackThis 2.0.2-->"C:\Program Files\trend micro\HijackThis.exe" /uninstall
Hotfix for Microsoft .NET Framework 3.5 SP1 (KB953595)-->C:\Windows\system32\msiexec.exe /package {CE2CDD62-0124-36CA-84D3-9F4DCF5C5BD9} /uninstall  /qb+ REBOOTPROMPT=""
Hotfix for Microsoft .NET Framework 3.5 SP1 (KB958484)-->C:\Windows\system32\msiexec.exe /package {CE2CDD62-0124-36CA-84D3-9F4DCF5C5BD9} /uninstall {A7EEA2F2-BFCD-4A54-A575-7B81A786E658} /qb+ REBOOTPROMPT=""
ICQ6.5-->"C:\Program Files\InstallShield Installation Information\{60DE4033-9503-48D1-A483-7846BD217CA9}\setup.exe" -runfromtemp -l0x0009 -removeonly
imagine digital freedom - Samsung-->MsiExec.exe /X{00AF10C1-44BD-4862-9D7F-24E6BA3E87FD}
IncrediMail 2.0-->C:\Program Files\IncrediMail\Bin\ImSetup.exe /uninstallProduct /addon:incredimail
IncrediMail-->MsiExec.exe /X{9B095F52-3E7C-4B90-9839-81C0C66177CA}
Intel PROSet Wireless-->Intel PROSet Wireless
Intel® Matrix Storage Manager-->C:\Windows\system32\imsmudlg.exe -uninstall
iTunes-->MsiExec.exe /I{5EFCBB42-36AB-4FF9-B90C-E78C7B9EE7B3}
Java(TM) 6 Update 13-->MsiExec.exe /X{26A24AE4-039D-4CA4-87B4-2F83216011FF}
Junk Mail filter update-->MsiExec.exe /I{4DE3E3D9-AE81-45DE-9195-3015F7B1DBF3}
kikin Plugin (Foto-Mosaik-Edda Edition) 1.11-->C:\Program Files\kikin\uninst.exe
KONICA MINOLTA magicolor 2430DL-->MUINST_U.EXE /PRN:"KONICA MINOLTA magicolor 2430DL"
LabelPrint-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\engine\6\INTEL3~1\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{C59C179C-668D-49A9-B6EA-0121CCFC1243}\setup.exe"  -uninstall
Last.fm 1.5.4.24567-->"C:\Program Files\Last.fm\unins000.exe"
LightScribe System Software  1.12.37.1-->MsiExec.exe /X{004C5DA2-2051-4D25-94BA-51CF810C91EB}
Malwarebytes' 
Anti-Malware-->"C:\Program Files\Malwarebytes' Anti-Malware\unins000.exe"
Microsoft .NET Framework 3.5 Language Pack SP1 - DEU-->C:\Windows\Microsoft.NET\Framework\v3.5\Microsoft .NET Framework 3.5 Language Pack SP1 - deu\setup.exe
Microsoft 
.NET Framework 3.5 Language Pack SP1 - deu-->MsiExec.exe /I{052FDD78-A6EA-3187-8386-C82F4CA3A929}
Microsoft .NET Framework 3.5 SP1-->C:\Windows\Microsoft.NET\Framework\v3.5\Microsoft .NET Framework 3.5 SP1\setup.exe
Microsoft 
.NET Framework 3.5 SP1-->MsiExec.exe /I{CE2CDD62-0124-36CA-84D3-9F4DCF5C5BD9}
Microsoft Office 2003 Web Components-->MsiExec.exe /I{90A40407-6000-11D3-8CFE-0150048383C9}
Microsoft Office 2007 Primary Interop Assemblies-->MsiExec.exe /X{50120000-1105-0000-0000-0000000FF1CE}
Microsoft Office Access MUI (German) 2007-->MsiExec.exe /X{90120000-0015-0407-0000-0000000FF1CE}
Microsoft Office Excel MUI (German) 2007-->MsiExec.exe /X{90120000-0016-0407-0000-0000000FF1CE}
Microsoft Office Live Add-in 1.3-->MsiExec.exe /I{57F0ED40-8F11-41AA-B926-4A66D0D1A9CC}
Microsoft Office Outlook Connector-->MsiExec.exe /I{95120000-0120-0407-0000-0000000FF1CE}
Microsoft Office Outlook MUI (German) 2007-->MsiExec.exe /X{90120000-001A-0407-0000-0000000FF1CE}
Microsoft Office PowerPoint MUI (German) 2007-->MsiExec.exe /X{90120000-0018-0407-0000-0000000FF1CE}
Microsoft Office Professional Edition 2003-->MsiExec.exe /I{90110407-6000-11D3-8CFE-0150048383C9}
Microsoft Office Professional Hybrid 2007-->MsiExec.exe /X{91120000-0031-0000-0000-0000000FF1CE}
Microsoft Office Proof (English) 2007-->MsiExec.exe /X{90120000-001F-0409-0000-0000000FF1CE}
Microsoft Office Proof (French) 2007-->MsiExec.exe /X{90120000-001F-040C-0000-0000000FF1CE}
Microsoft Office Proof (German) 2007-->MsiExec.exe /X{90120000-001F-0407-0000-0000000FF1CE}
Microsoft Office Proof (Italian) 2007-->MsiExec.exe /X{90120000-001F-0410-0000-0000000FF1CE}
Microsoft Office Proofing (German) 2007-->MsiExec.exe /X{90120000-002C-0407-0000-0000000FF1CE}
Microsoft Office Publisher MUI (German) 2007-->MsiExec.exe /X{90120000-0019-0407-0000-0000000FF1CE}
Microsoft Office Shared MUI (German) 2007-->MsiExec.exe /X{90120000-006E-0407-0000-0000000FF1CE}
Microsoft Office Small Business Connectivity Components-->MsiExec.exe /X{A939D341-5A04-4E0A-BB55-3E65B386432D}
Microsoft Office Word MUI (German) 2007-->MsiExec.exe /X{90120000-001B-0407-0000-0000000FF1CE}
Microsoft Search Enhancement Pack-->MsiExec.exe /X{4CBA3D4C-8F51-4D60-B27E-F6B641C571E7}
Microsoft Silverlight-->MsiExec.exe /X{89F4137D-6C26-4A84-BDB8-2E5A4BB71E00}
Microsoft SOAP Toolkit 2.0 SP2-->MsiExec.exe /I{36BEAD11-8577-49AD-9250-E06A50AE87B0}
Microsoft SQL Server 2005 Compact Edition [ENU]-->MsiExec.exe /I{F0B430D1-B6AA-473D-9B06-AA3DD01FD0B8}
Microsoft SQL Server 2005 Express Edition (MSSMLBIZ)-->MsiExec.exe /I{028ED9C4-25EE-4DEE-9CF4-91034BC89B18}
Microsoft SQL Server 2005-->"C:\Program Files\Microsoft SQL Server\90\Setup Bootstrap\ARPWrapper.exe" /Remove
Microsoft SQL Server Native Client
-->MsiExec.exe /I{7FB12670-0F93-4E1E-B2F5-4F339199A03A}
Microsoft SQL Server VSS Writer-->MsiExec.exe /I{849A32C3-E75A-4791-9B11-E568BA3525A4}
Microsoft Sync Framework Runtime Native v1.0 (x86)-->MsiExec.exe /I{8A74E887-8F0F-4017-AF53-CBA42211AAA5}
Microsoft Sync Framework Services Native v1.0 (x86)-->MsiExec.exe /I{BD64AF4A-8C80-4152-AD77-FCDDF05208AB}
Microsoft Visual C++ 2005 ATL Update kb973923 - x86 8.0.50727.4053-->MsiExec.exe /X{770657D0-A123-3C07-8E44-1C83EC895118}
Microsoft Visual C++ 2005 Redistributable-->MsiExec.exe /X{7299052b-02a4-4627-81f2-1818da5d550d}
Microsoft Visual C++ 2008 ATL Update kb973924 - x86 9.0.30729.4148-->MsiExec.exe /X{002D9D5E-29BA-3E6D-9BC4-3D7D6DBC735C}
Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.17-->MsiExec.exe /X{9A25302D-30C0-39D9-BD6F-21E6EC160475}
Microsoft WSE 3.0 Runtime-->MsiExec.exe /X{E3E71D07-CD27-46CB-8448-16D4FB29AA13}
Mozilla Firefox (3.0)-->C:\Program Files\Mozilla Firefox\uninstall\helper.exe
MSVCRT
-->MsiExec.exe /I{22B775E7-6C42-4FC5-8E10-9A5E3257BD94}
MSXML 4.0 SP2 (KB954430)-->MsiExec.exe /I{86493ADD-824D-4B8E-BD72-8C5DCDC52A71}
NAVIGON Fresh 1.6.0-->C:\Program Files\NAVIGON\NAVIGON Fresh\uninst.exe
NVIDIA Drivers
-->C:\Windows\system32\nvuninst.exe UninstallGUI
NVIDIA PhysX
-->MsiExec.exe /X{DD1865F0-AD73-40FB-B23E-1822E02396FF}
PDF Settings-->MsiExec.exe /I{AC5B0C19-D851-42F4-BDA0-410ECF7F70A5}
Play AVStation-->C:\PROGRA~1\COMMON~1\INSTAL~1\Driver\10\INTEL3~1\IDriver.exe /M{955597D8-E5E1-474D-B647-60AC44566D24} /l1031 
PlayCamera
-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\PROFES~1\RunTime\09\01\Intel32\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{804F1285-8CBF-408D-8CDC-D4D40003B2E4}\setup.exe" -l0x7 
PowerDirector
-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\engine\6\INTEL3~1\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{CB099890-1D5F-11D5-9EA9-0050BAE317E1}\setup.exe"  -uninstall
PowerDVD
-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\engine\6\INTEL3~1\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{6811CAA0-BF12-11D4-9EA1-0050BAE317E1}\setup.exe"  -uninstall
PowerProducer
-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\engine\6\INTEL3~1\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{B7A0CE06-068E-11D6-97FD-0050BACBF861}\setup.exe"  -uninstall
QuickTime
-->MsiExec.exe /I{216AB108-2AE1-4130-B3D5-20B2C4C80F8F}
Realtek High Definition Audio Driver-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\PROFES~1\RunTime\11\50\Intel32\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{F132AF7F-7BCA-4EDE-8A7C-958108FE7DBC}\setup.exe"  -removeonly
Samsung Magic Doctor
-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\PROFES~1\RunTime\0701\Intel32\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{32D6A58F-9659-446C-BBFC-E6F2B41F24DC}\Setup.exe" -l0x9 Remove
SAMSUNG Mobile Composite Device Software
-->C:\Windows\system32\Samsung_USB_Drivers\6\SSBCUninstall.exe
SAMSUNG Mobile Modem Driver Set
-->C:\Windows\system32\Samsung_USB_Drivers\3\SSCDUninstall.exe
Samsung Mobile phone USB driver Software
-->C:\Windows\system32\Samsung_USB_Drivers\5\SSSDUninstall.exe
SAMSUNG Mobile USB Modem 1.0 Software
-->C:\Windows\system32\Samsung_USB_Drivers\1\SS_Uninstall.exe
SAMSUNG Mobile USB Modem Software
-->C:\Windows\system32\Samsung_USB_Drivers\2\SSM_Uninstall.exe
Samsung PC Studio 3 USB Driver Installer
-->"C:\Program Files\InstallShield Installation Information\{EBA29752-DDD2-4B62-B2E3-9841F92A3E3A}\setup.exe" -runfromtemp -l0x0007 -removeonly
Samsung PC Studio 3
-->"C:\Program Files\InstallShield Installation Information\{C4A4722E-79F9-417C-BD72-8D359A090C97}\setup.exe" -runfromtemp -l0x0007 -removeonly
Samsung Recovery Solution III
-->"C:\Program Files\InstallShield Installation Information\{145DE957-0679-4A2A-BB5C-1D3E9808FAB2}\setup.exe" -runfromtemp -l0x0007 -removeonly
Samsung Update Plus
-->C:\PROGRA~1\COMMON~1\INSTAL~1\Driver\10\INTEL3~1\IDriver.exe /M{685707A4-911C-468D-BFC4-64A50E5E3A0C} /l1031 
Search Settings 1.2.1
-->MsiExec.exe /X{0B1AAC97-8563-41D9-AE47-58E6A222F0E1}
Security Update for 2007 Microsoft Office System (KB951550)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {B243E9A5-ED77-4F1B-B338-2486FD82DC85}
Security Update for 2007 Microsoft Office System (KB951944)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {797AE457-BA17-4BBC-B501-25FB3A0103C7}
Security Update for 2007 Microsoft Office System (KB969559)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {69F52148-9BF6-4CDC-BF76-103DEAF3DD08}
Security Update for 2007 Microsoft Office System (KB969679)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {C66E4A6C-6E07-4C63-8CCD-2493B5087C73}
Security Update for Microsoft Office Excel 2007 (KB969682)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {C03803BD-745A-46F8-8557-817DED578780}
Security Update for Microsoft Office Outlook 2007 (KB972363)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {120BE9A0-9B09-4855-9E0C-7DEE45CB03C0}
Security Update for Microsoft Office PowerPoint 2007 (KB957789)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {7559E742-FF9F-4FAE-B279-008ED296CB4D}
Security Update for Microsoft Office Publisher 2007 (KB969693)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {7BE67088-1EB3-4569-8E75-DDAFBF61BC4E}
Security Update for Microsoft Office system 2007 (972581)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {3D019598-7B59-447A-80AE-815B703B84FF}
Security Update for Microsoft Office system 2007 (KB969613)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {5ECEB317-CBE9-4E08-AB10-756CB6F0FB6C}
Security Update for Microsoft Office system 2007 (KB974234)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {FCD742B9-7A55-44BC-A776-F795F21FEDDC}
Security Update for Microsoft Office Visio Viewer 2007 (KB973709)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {71127777-8B2C-4F97-AF7A-6CF8CAC8224D}
Security Update for Microsoft Office Word 2007 (KB969604)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {CF3D6499-709C-43D0-8908-BC5652656050}
Skype™ 3.8-->MsiExec.exe /X{5C82DAE5-6EB0-4374-9254-BE3319BA4E82}
Spybot - Search & Destroy-->"C:\Program Files\Spybot - Search & Destroy\unins000.exe"
Synaptics Pointing Device Driver-->rundll32.exe "C:\Program Files\Synaptics\SynTP\SynISDLL.dll",standAloneUninstall
The KMPlayer 
(remove only)-->"C:\Program Files\The KMPlayer\uninstall.exe"
Uninstall 1.0.0.1-->"C:\Program Files\Common Files\DVDVideoSoft\unins000.exe"
Unterstützungsdateien für das Microsoft SQL Server-Setup (Englisch)-->MsiExec.exe /X{07629207-FAA0-4F1A-8092-BF5085BE511F}
Update for 2007 Microsoft Office System (KB967642)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {C444285D-5E4F-48A4-91DD-47AAAA68E92D}
Update for Microsoft .NET Framework 3.5 SP1 (KB963707)-->C:\Windows\system32\msiexec.exe /package {CE2CDD62-0124-36CA-84D3-9F4DCF5C5BD9} /uninstall {B2AE9C82-DC7B-3641-BFC8-87275C4F3607} /qb+ REBOOTPROMPT=""
Update for Outlook 2007 Junk Email Filter (KB974810)-->msiexec /package {91120000-0031-0000-0000-0000000FF1CE} /uninstall {C05FBAD5-A211-4E86-BB51-7E07B80C9233}
Update für Microsoft Office Excel 2007 Help (KB963678)-->msiexec /package {90120000-0016-0407-0000-0000000FF1CE} /uninstall {BEC163EC-7A83-48A1-BFB6-3BF47CC2F8CF}
Update für Microsoft Office Outlook 2007 Help (KB963677)-->msiexec /package {90120000-001A-0407-0000-0000000FF1CE} /uninstall {F6828576-6F79-470D-AB50-69D1BBADBD30}
Update für Microsoft Office Powerpoint 2007 Help (KB963669)-->msiexec /package {90120000-0018-0407-0000-0000000FF1CE} /uninstall {EA160DA3-E9B5-4D03-A518-21D306665B96}
Update für Microsoft Office Word 2007 Help (KB963665)-->msiexec /package {90120000-001B-0407-0000-0000000FF1CE} /uninstall {38472199-D7B6-4833-A949-10E4EE6365A1}
User Guide-->RunDll32 C:\PROGRA~1\COMMON~1\INSTAL~1\PROFES~1\RunTime\0701\Intel32\Ctor.dll,LaunchSetup "C:\Program Files\InstallShield Installation Information\{BAE68339-B0F6-4D33-9554-5A3DB2DFF5DA}\setup.exe" -l0x9 Remove
VC80CRTRedist 
- 8.0.50727.762-->MsiExec.exe /I{767CC44C-9BBC-438D-BAD3-FD4595DD148B}
Vimicro UVC Camera-->C:\Program Files\InstallShield Installation Information\{71A51B09-E7D3-11DB-A386-005056C00008}\setup.exe -runfromtemp -l0x0009 -removeonly
VLC media player 0.9.8a
-->C:\Program Files\VideoLAN\VLC\uninstall.exe
WIDCOMM Bluetooth Software 6.0.1.6300
-->MsiExec.exe /X{03D1988F-469F-4843-8E6E-E5FE9D17889D}
Windows Live Anmelde-Assistent-->MsiExec.exe /I{52B97218-98CB-4B8B-9283-D213C85E1AA4}
Windows Live Call-->MsiExec.exe /I{5FC68772-6D56-41C6-9DF1-24E868198AE6}
Windows Live Communications Platform-->MsiExec.exe /I{3B4E636E-9D65-4D67-BA61-189800823F52}
Windows Live Essentials-->C:\Program Files\Windows Live\Installer\wlarp.exe
Windows Live Essentials
-->MsiExec.exe /I{91E04CA7-0B13-4F8C-AA4D-2A573AC96D19}
Windows Live Family Safety-->MsiExec.exe /X{54B1E5A3-1B29-4582-A226-172A1FC7BA6C}
Windows Live Fotogalerie-->MsiExec.exe /X{119B7481-0216-40D2-A5CC-C3E1F461ECC1}
Windows Live Mail-->MsiExec.exe /I{5A166C0B-9557-4364-A057-F946D674E6AC}
Windows Live Messenger-->MsiExec.exe /X{837B6259-6FF5-4E66-87C1-A5A15ED36FF4}
Windows Live Movie Maker-Betaversion-->MsiExec.exe /X{FE6E1AF6-6B88-44FE-8101-84AE6A52B393}
Windows Live Sync-->MsiExec.exe /X{ED636101-1959-4360-8BF7-209436E7DEE4}
Windows Live Toolbar-->MsiExec.exe /X{70B7A167-0B88-445D-A3EA-97C73AA88CAC}
Windows Live Writer-->MsiExec.exe /X{81821BF8-DA20-4F8C-AA87-F70A274828D4}
Windows Live-Uploadtool-->MsiExec.exe /I{205C6BDD-7B73-42DE-8505-9A093F35A238}
WinRAR-->C:\Program Files\WinRAR\uninstall.exe

======Security center information======

AS: 
Spybot - Search and Destroy
AS: Windows Defender

======System event log======

Computer Name: ****-PC
Event Code
: 18
Message
: Installationsbereit: Die folgenden Updates wurden heruntergeladen und können installiert werden. Diese Updates sollen laut Zeitplan am ?Donnerstag, ?5. ?November ?2009 um 03:00 auf diesem Computer installiert werden: 
- 
Update für die Kompatibilitätsansichtsliste für Internet Explorer*8 für Windows Vista (KB975364)
Record Number: 89247
Source Name
: Microsoft-Windows-WindowsUpdateClient
Time Written
: 20091104152909.261400-000
Event Type
: Informationen
User
: NT-AUTORITÄT\SYSTEM 

Alt 04.11.2009, 17:22   #5
Vanelein
 
Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren! - Standard

Teil 3.1


PHP-Code:
Computer Name: ****-PC
Event Code
: 18
Message
: Installationsbereit: Die folgenden Updates wurden heruntergeladen und können installiert werden. Diese Updates sollen laut Zeitplan am ?Donnerstag, ?5. ?November ?2009 um 03:00 auf diesem Computer installiert werden: 
- 
Update für die Kompatibilitätsansichtsliste für Internet Explorer 8 für Windows Vista (KB975364)
- 
Sicherheitsupdate für Jscript 5.8 für Windows Vista (KB971961)
Record Number: 89248
Source Name
: Microsoft-Windows-WindowsUpdateClient
Time Written
: 20091104152909.261400-000
Event Type
: Informationen
User
: NT-AUTORITÄT\SYSTEM

Computer Name
: *****-PC
Event Code
: 18
Message
: Installationsbereit: Die folgenden Updates wurden heruntergeladen und können installiert werden. Diese Updates sollen laut Zeitplan am ?Donnerstag, ?5. ?November ?2009 um 03:00 auf diesem Computer installiert werden: 
- 
Update für die Kompatibilitätsansichtsliste für Internet Explorer 8 für Windows Vista (KB975364)
- 
Sicherheitsupdate für Jscript 5.8 für Windows Vista (KB971961)
Record Number: 89249
Source Name
: Microsoft-Windows-WindowsUpdateClient
Time Written
: 20091104152951.646600-000
Event Type
: Informationen
User
: NT-AUTORITÄT\SYSTEM

Computer Name
: Vane-PC
Event Code
: 7036
Message
: Dienst "Windows Modules Installer" befindet sich jetzt im Status "Beendet".
Record Number: 89250
Source Name
: Service Control Manager
Time Written
: 20091104153302.000000-000
Event Type
: Informationen
User
: 

Computer Name: Vane-PC
Event Code
: 7036
Message
: Dienst "WinHTTP-Web Proxy Auto-Discovery-Dienst" befindet sich jetzt im Status "Beendet".
Record Number: 89251
Source Name
: Service Control Manager
Time Written
: 20091104153852.000000-000
Event Type
: Informationen
User
: 

=====
Application event log=====

Computer Name: Vane-PC
Event Code
: 8194
Message
: Der Wiederherstellungspunkt wurde erfolgreich erstellt (Prozess = C:\Windows\system32\msiexec.exe /V; Beschreibung = Removed Bonjour).
Record Number: 185432
Source Name
: System Restore
Time Written
: 20091104151643.000000-000
Event Type
: Informationen
User
: 

Computer Name: Vane-PC
Event Code
: 11725
Message
: Produkt: Bonjour -- Das Entfernen ist fehlgeschlagen.
Record Number: 185433
Source Name
: MsiInstaller
Time Written
: 20091104151645.000000-000
Event Type
: Informationen
User
: Vane-PC\Vane

Computer Name
: Vane-PC
Event Code
: 1034
Message
: Das Produkt wurde durch Windows Installer deinstalliert. Produktname: Bonjour. Produktversion: 1.0.106. Produktsprache: 1031. Erfolg- bzw. Fehlerstatus der Deinstallation: 1602.
Record Number
: 185434
Source Name
: MsiInstaller
Time Written
: 20091104151645.000000-000
Event Type
: Informationen
User
: Vane-PC\Vane

Computer Name
: Vane-PC
Event Code
: 8224
Message
: Der VSS-Dienst wird aufgrund eines Leerlaufzeitlimits heruntergefahren. 
Record Number: 185435
Source Name
: VSS
Time Written
: 20091104152244.000000-000
Event Type
: Informationen
User
: 

Computer Name: Vane-PC
Event Code
: 5
Message
: Unsupported service control request (see data below)
Record Number: 185436
Source Name
: LightScribeService
Time Written
: 20091104154658.000000-000
Event Type
: Informationen
User
: 

=====
Security event log=====

Computer Name: Vane-PC
Event Code
: 5038
Message
: Die Codeintegrität hat festgestellt, dass der Abbildhash einer Datei nicht gültig ist. Die Datei wurde möglicherweise durch eine nicht autorisierte Änderung beschädigt. Dieses Problem kann auch auf einen potenziellen Fehler des Datenträgergeräts hinweisen.

Dateiname:    \Device\HarddiskVolume2\Windows\System32\drivers\tcpip.sys    
Record Number
: 12634
Source Name
: Microsoft-Windows-Security-Auditing
Time Written
: 20091104154649.333600-000
Event Type
: Überwachung gescheitert
User
: 

Computer Name: Vane-PC
Event Code
: 5038
Message
: Die Codeintegrität hat festgestellt, dass der Abbildhash einer Datei nicht gültig ist. Die Datei wurde möglicherweise durch eine nicht autorisierte Änderung beschädigt. Dieses Problem kann auch auf einen potenziellen Fehler des Datenträgergeräts hinweisen.

Dateiname:    \Device\HarddiskVolume2\Windows\System32\drivers\tcpip.sys    
Record Number
: 12635
Source Name
: Microsoft-Windows-Security-Auditing
Time Written
: 20091104154649.474000-000
Event Type
: Überwachung gescheitert
User
: 

Computer Name: Vane-PC
Event Code
: 5038
Message
: Die Codeintegrität hat festgestellt, dass der Abbildhash einer Datei nicht gültig ist. Die Datei wurde möglicherweise durch eine nicht autorisierte Änderung beschädigt. Dieses Problem kann auch auf einen potenziellen Fehler des Datenträgergeräts hinweisen.

Dateiname:    \Device\HarddiskVolume2\Windows\System32\drivers\tcpip.sys    
Record Number
: 12636
Source Name
: Microsoft-Windows-Security-Auditing
Time Written
: 20091104154649.630000-000
Event Type
: Überwachung gescheitert
User
: 

Computer Name: Vane-PC
Event Code
: 5038
Message
: Die Codeintegrität hat festgestellt, dass der Abbildhash einer Datei nicht gültig ist. Die Datei wurde möglicherweise durch eine nicht autorisierte Änderung beschädigt. Dieses Problem kann auch auf einen potenziellen Fehler des Datenträgergeräts hinweisen.

Dateiname:    \Device\HarddiskVolume2\Windows\System32\drivers\tcpip.sys    
Record Number
: 12637
Source Name
: Microsoft-Windows-Security-Auditing
Time Written
: 20091104154649.786000-000
Event Type
: Überwachung gescheitert
User
: 

Computer Name: ****-PC
Event Code
: 5038
Message
: Die Codeintegrität hat festgestellt, dass der Abbildhash einer Datei nicht gültig ist. Die Datei wurde möglicherweise durch eine nicht autorisierte Änderung beschädigt. Dieses Problem kann auch auf einen potenziellen Fehler des Datenträgergeräts hinweisen.

Dateiname:    \Device\HarddiskVolume2\Windows\System32\drivers\tcpip.sys    
Record Number
: 12638
Source Name
: Microsoft-Windows-Security-Auditing
Time Written
: 20091104154649.942000-000
Event Type
: Überwachung gescheitert
User
: 

======
Environment variables======

"ComSpec"=%SystemRoot%\system32\cmd.exe
"FP_NO_HOST_CHECK"=NO
"OS"=Windows_NT
"Path"=%SystemRoot%\system32;%SystemRoot%;%SystemRoot%\System32\Wbem;C:\Program Files\Intel\WiFi\bin\;C:\Program Files\Microsoft SQL Server\90\Tools\binn\;C:\Program Files\QuickTime\QTSystem\;C:\Program Files\Samsung\Samsung PC Studio 3\;C:\Program Files\Common Files\DivX Shared\
"PATHEXT"=.COM;.EXE;.BAT;.CMD;.VBS;.VBE;.JS;.JSE;.WSF;.WSH;.MSC
"PROCESSOR_ARCHITECTURE"=x86
"TEMP"=%SystemRoot%\TEMP
"TMP"=%SystemRoot%\TEMP
"USERNAME"=SYSTEM
"windir"=%SystemRoot%
"PROCESSOR_LEVEL"=6
"PROCESSOR_IDENTIFIER"=x86 Family 6 Model 23 Stepping 6, GenuineIntel
"PROCESSOR_REVISION"=1706
"NUMBER_OF_PROCESSORS"=2
"TRACE_FORMAT_SEARCH_PATH"=\\NTREL202.ntdev.corp.microsoft.com\4F18C3A5-CA09-4DBD-B6FC-219FDD4C6BE0\TraceFormat
"DFSTRACINGON"=FALSE
"CLASSPATH"=.;C:\Program Files\Java\jre6\lib\ext\QTJava.zip
"QTJAVA"=C:\Program Files\Java\jre6\lib\ext\QTJava.zip

-----------------EOF----------------- 


Antwort

Themen zu Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren!
absoluter, andauernd, anleitung, dauernd, eingeschränkte, einzelne, einzelnen, folge, folgendes, größte, interne, internet-explorer, liebe, lieben, melde, meldet, meldungen, mozilla, nenne, surfe, surfen, tr/crypt.zpack.gen, vermutlich, viren, öffnet


Ähnliche Themen: Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren!


  1. Werbung, vermutlich durch Okay Freedom und googleads.g.doubleclick.net
    Log-Analyse und Auswertung - 23.08.2015 (59)
  2. Malware trotz Neuinstallation vermutlich noch vorhanden
    Log-Analyse und Auswertung - 18.08.2015 (5)
  3. Win8: Laptop vermutlich durch Trojaner lahmgelegt
    Plagegeister aller Art und deren Bekämpfung - 29.05.2015 (12)
  4. Massive Lagspikes, vermutlich verursacht durch Chrome
    Log-Analyse und Auswertung - 28.04.2015 (13)
  5. Fastsearchings.info und vermutlich weitere Viren
    Plagegeister aller Art und deren Bekämpfung - 15.07.2014 (15)
  6. Viren vermutlich auf externer Festplatte
    Plagegeister aller Art und deren Bekämpfung - 28.03.2013 (2)
  7. Schadsoftware eingefangen (Vermutlich noch nicht erkannt)
    Plagegeister aller Art und deren Bekämpfung - 26.07.2012 (3)
  8. Nach GVU-Trojaner nur noch eingeschränkte Funktion sowie Meldung "roper0dun.exe"
    Plagegeister aller Art und deren Bekämpfung - 18.07.2012 (11)
  9. Vermutlich Keylogger durch Sch...tool eingefangen
    Plagegeister aller Art und deren Bekämpfung - 03.06.2012 (1)
  10. abnow.com bzw. ZeroAccess trotz Entfernung vermutlich noch auf PC
    Plagegeister aller Art und deren Bekämpfung - 05.04.2012 (2)
  11. Eingeschränkte Antivirenprogramme durch Virus
    Log-Analyse und Auswertung - 08.03.2012 (1)
  12. pc hat vermutlich viren, spy und Co. :(
    Log-Analyse und Auswertung - 08.07.2011 (9)
  13. Vermutlich Problem mit Viren oder Malware
    Log-Analyse und Auswertung - 07.03.2011 (35)
  14. Probleme mit meinem PC - vermutlich Viren
    Plagegeister aller Art und deren Bekämpfung - 21.11.2010 (9)
  15. Vermutlich Trojaner durch behörden
    Log-Analyse und Auswertung - 29.07.2009 (7)
  16. Vermutlich Viren/Trojaner...probleme mit div. Popups
    Log-Analyse und Auswertung - 27.01.2008 (1)
  17. Computer läuft vermutlich durch Viren langsam
    Plagegeister aller Art und deren Bekämpfung - 27.07.2007 (27)

Zum Thema Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren! - Hallo meine Lieben, hier meldet sich ein absoluter Computer-nicht-checker und habe folgendes Problem. Ich bekomme andauernd Virenmeldungen zu viele um jetzt jeden einzelnen zu nennen aber das größte Problme ist - Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren!...
Archiv
Du betrachtest: Nur noch eingeschränkte Administrationsrechte vermutlich durch Viren! auf Trojaner-Board

Search Engine Optimization by vBSEO ©2011, Crawlability, Inc.